Introduction
Security Operations play a vital role in protecting modern businesses from digital threats and security risks.
As organizations rely more heavily on technology, protecting their systems and information becomes increasingly important.
Security Operations help companies identify suspicious activities, respond to incidents, and reduce potential damage.
They bring together skilled professionals, security tools, and established procedures to maintain a safe digital environment.
A well-managed security strategy allows businesses to operate confidently while protecting valuable assets and customer information.
1. Understanding Security Operations
Security Operations refer to the daily activities involved in monitoring, managing, and improving an organization’s security.
These activities focus on protecting networks, applications, devices, and sensitive business information from potential threats.
Security teams continuously review system activity to identify unusual behavior before it causes serious problems.
They also establish procedures for investigating alerts and handling security incidents effectively.
The main objective is to reduce risks while keeping business operations stable and reliable.
Security Operations combine technology, human expertise, and practical policies to achieve this goal.
Every organization can benefit from security practices that match its size, industry, and specific requirements.
A clear operational strategy creates a stronger foundation for long-term cybersecurity.
2. Importance of Security Operations
Security Operations are essential because cyberattacks can interrupt services, expose confidential information, and damage business reputations.
Organizations face risks such as phishing, ransomware, unauthorized access, and data theft.
Without proper monitoring, these threats may remain unnoticed until significant damage has occurred.
A dedicated security approach helps businesses recognize warning signs and respond before situations become more serious.
It also supports regulatory compliance and helps maintain customer confidence.
Effective security practices can reduce financial losses associated with cyber incidents and operational downtime.
They encourage employees to follow safer procedures when handling information and using company systems.
For these reasons, Security Operations are an important part of responsible business management.
3. The Role of a Security Operations Center
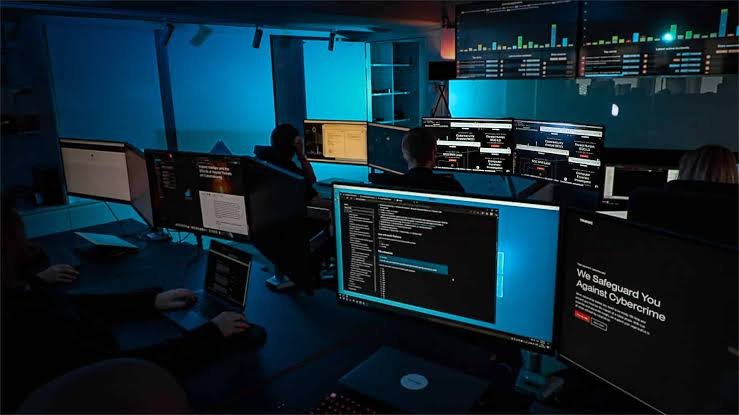
A Security Operations Center, commonly known as a SOC, coordinates security monitoring and incident response activities.
It may operate within an organization or be provided by an external security service.
SOC analysts review alerts generated by security software and investigate activities that appear suspicious.
They use information from networks, endpoints, cloud services, and other systems to understand possible threats.
When an incident is confirmed, the team follows established procedures to contain and investigate it.
The SOC also documents findings and shares important information with relevant teams.
Depending on the organization, its operations may run continuously throughout the day and night.
A well-organized SOC improves visibility and helps businesses manage security incidents more efficiently.
4. Key Responsibilities of Security Operations Teams
Security Operations teams perform several tasks that support the protection of digital environments.
They monitor system activity, investigate alerts, manage vulnerabilities, and help enforce security policies.
Another important responsibility is maintaining accurate records of incidents and response actions.
These records help teams understand what happened and identify opportunities for improvement.
Security professionals may also review access permissions to ensure users have appropriate levels of access.
They collaborate with IT departments to address weaknesses in devices, applications, and infrastructure.
Regular assessments help confirm whether existing security controls are working as intended.
By managing these responsibilities consistently, teams can improve an organization’s overall security posture.
5. Threat Detection and Continuous Monitoring
Threat detection involves identifying activities that may indicate an attack or unauthorized system access.
Continuous monitoring allows security teams to examine events as they occur across connected environments.
Specialized tools collect logs and highlight patterns that deserve further investigation.
For example, repeated failed login attempts may suggest someone is trying to access an account without permission.
Unusual file transfers or unexpected changes to system settings can also require attention.
Security analysts evaluate these signals to distinguish genuine threats from harmless activity.
Early detection gives organizations more time to investigate problems and limit their potential impact.
Consistent monitoring is therefore a fundamental element of effective Security Operations.
6. Incident Response and Recovery
Incident response describes the process of managing a security event from initial detection through recovery.
The process typically includes preparation, identification, containment, removal of the threat, and restoration of affected systems.
Security teams first determine the nature and severity of an incident.
They then take appropriate steps to prevent the problem from spreading to additional systems.
After removing the threat, specialists restore services and verify that systems are operating safely.
Organizations should also investigate the underlying cause to prevent similar incidents in the future.
Clear communication and accurate documentation are important throughout the response process.
A tested incident response plan helps businesses recover more effectively when security problems occur.
7. Essential Security Operations Tools
Security Operations teams use different tools to monitor systems, investigate threats, and protect important information.
Security Information and Event Management platforms, or SIEM systems, collect and analyze security logs from multiple sources.
Endpoint Detection and Response tools help identify and investigate suspicious activity on computers and servers.
Threat intelligence platforms provide information about emerging attacks, malicious infrastructure, and known threat actors.
Vulnerability scanners help identify outdated software and weaknesses that attackers might exploit.
Automation tools can assist with repetitive tasks, alert handling, and selected response actions.
However, tools are most effective when configured correctly and supported by knowledgeable professionals.
Choosing suitable technologies helps organizations build a practical and manageable security environment.
8. The Role of Automation and Artificial Intelligence
Automation can make Security Operations more efficient by reducing the time spent on repetitive activities.
For example, automated workflows can enrich alerts with additional information or assign incidents to the appropriate team.
Artificial intelligence can help analyze large volumes of security data and identify unusual patterns.
These capabilities may allow analysts to prioritize important alerts more quickly.
Automation can also support consistent responses to well-understood security events.
However, automated systems may produce false alarms or misunderstand unusual but legitimate activity.
Human oversight remains necessary for complex investigations and high-impact decisions.
Combining automation with professional judgment can improve both efficiency and the quality of security decisions.
9. Common Challenges in Security Operations
Security Operations teams often face challenges that make protecting business systems more complicated.
A high volume of alerts can overwhelm analysts and make important warnings harder to recognize.
Staff shortages and limited budgets may also restrict an organization’s ability to respond quickly.
Complex technology environments can create visibility gaps across cloud services, remote devices, and business applications.
Attackers continually change their methods, requiring security professionals to update their knowledge and defenses.
Poorly configured tools may generate unnecessary alerts or fail to detect relevant activity.
Organizations can address these challenges through training, improved processes, and careful technology planning.
Regular reviews help teams identify weaknesses and make practical improvements over time.
10. Security Operations Best Practices
Strong Security Operations begin with clear policies, defined responsibilities, and a realistic understanding of business risks.
Organizations should keep operating systems and applications updated to reduce exposure to known vulnerabilities.
Multi-factor authentication adds another layer of protection to important accounts.
Access should be limited according to each employee’s responsibilities and business requirements.
Security teams should review logs, test incident response plans, and maintain reliable backups.
Employee awareness training can reduce risks associated with phishing and unsafe online behavior.
Regular security assessments help determine whether controls remain effective as business needs change.
Following these practices creates a more consistent and resilient approach to protecting digital assets.
11. Measuring Security Operations Performance
Measuring performance helps organizations understand whether their security processes are producing useful results.
One common measurement is mean time to detect, which tracks how long it takes to identify a security incident.
Mean time to respond measures the time required to begin or complete an appropriate response, depending on the defined metric.
Teams may also examine alert accuracy, investigation backlogs, and the number of recurring incidents.
These measurements can reveal delays, resource shortages, and weaknesses in existing workflows.
However, numbers should always be considered alongside the severity and context of security events.
A low incident count does not necessarily mean an organization is well protected.
Meaningful performance reviews help leaders make informed decisions about staffing, tools, and future improvements.
12. The Future of Security Operations
Security Operations will continue to evolve as organizations adopt cloud platforms, connected devices, and new digital services.
Security teams will need to protect increasingly distributed systems and manage more complex access requirements.
Artificial intelligence and automation are likely to play a growing role in detection and investigation.
At the same time, attackers may use advanced technologies to develop more convincing scams and sophisticated attacks.
Organizations will need to balance innovation with careful testing, governance, and human oversight.
Continuous training will remain important as security tools and threat techniques change.
Collaboration between security, IT, management, and employees will help organizations respond to emerging risks.
Businesses that adapt their security strategies can improve resilience and prepare for future challenges.
Conclusion
Security Operations are a fundamental part of protecting modern organizations against digital threats.
They combine monitoring, threat detection, incident response, and continuous improvement to reduce security risks.
Effective teams rely on suitable tools, trained professionals, and well-defined procedures.
By addressing weaknesses and learning from security incidents, organizations can strengthen their defenses over time.
Investing in Security Operations helps businesses protect valuable information, maintain trust, and support reliable operations.
Frequently Asked Questions (FAQs)
1. What are Security Operations?
Security Operations involve monitoring, managing, and improving an organization’s defenses against cybersecurity threats. They include threat detection, incident investigation, vulnerability management, and security response activities.
2. What is the main purpose of a Security Operations Center?
A Security Operations Center monitors systems, investigates suspicious activity, and coordinates responses to security incidents. Its purpose is to help identify threats early and reduce their potential impact on the organization.
3. How can a business improve its Security Operations?
A business can improve Security Operations by using appropriate security tools, training employees, updating software, enforcing strong access controls, and regularly testing its incident response procedures. Continuous evaluation also helps identify areas that need improvement.